September 17, 2026
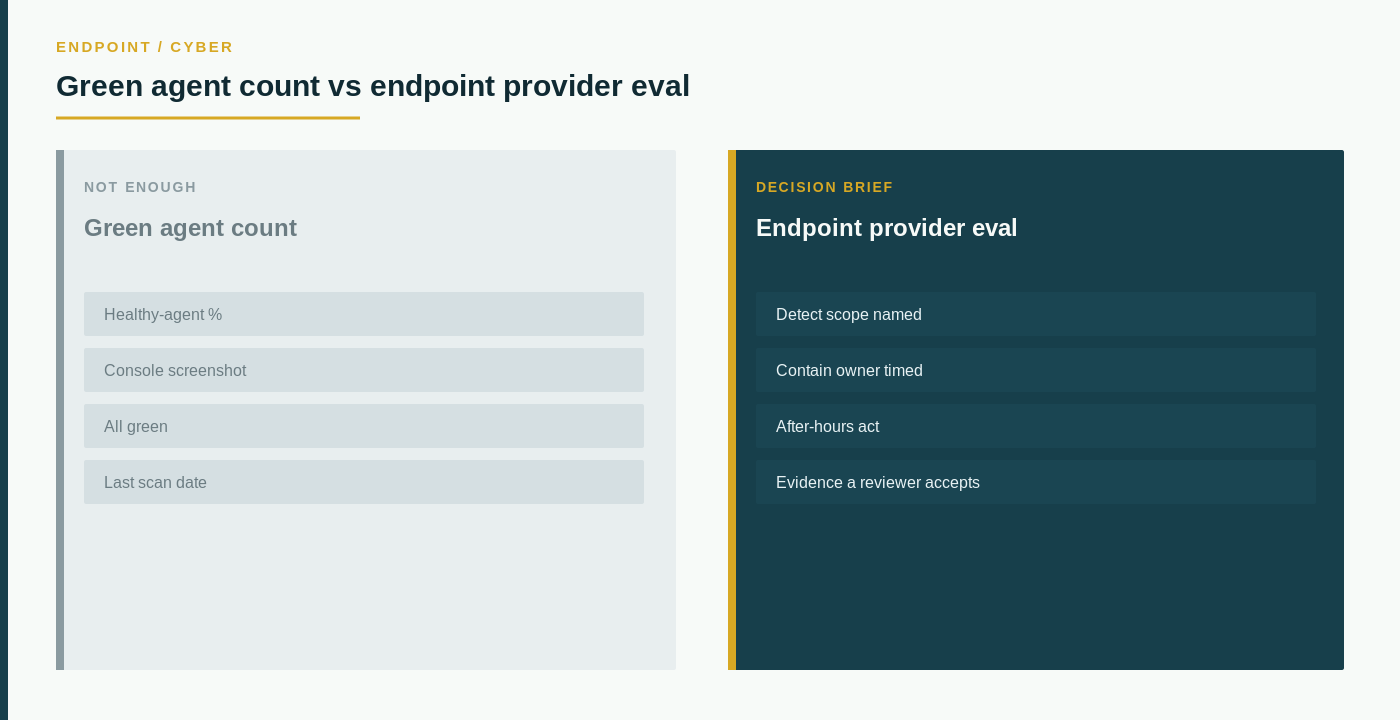
Concise answer: A green agent count is a snapshot — a healthy-agent percentage, a console screenshot, an “all green” claim, a last-scan date. An endpoint security provider evaluation is an operating decision: what is in detect scope, who owns contain and after-hours act, what evidence a later reviewer will accept, and how a failed agent is noticed. Treat the count as one input. Do not treat it as the evaluation.
Agent dashboards are good at coloring a fleet. They are not designed to tell you whether Monday’s ransomware path still gets contained.
The central principle is simple: a green agent count is a console artifact, while an endpoint security provider evaluation is an operating decision. Those questions are related. They are not interchangeable.
This page is an endpoint security provider evaluation brief, not a healthy-agent flyer. A green percentage, a console PNG, or a last-scan date can inform the conversation — they do not replace the eval. This evaluation concerns the endpoint provider you are about to keep or replace.
What a green agent count actually tells you
A green agent count usually arrives as a dashboard tile, a weekly PDF, or a “98% healthy” slide. It can be useful. It tells you how many endpoints reported in at a moment.
It does not tell you whether detect scope, contain ownership, or after-hours act will survive a real incident.
A green agent count may represent:
- A healthy percentage that never named what is in detect scope.
- A console screenshot that ignores offline, BYOD, and OT exceptions.
- An “all green” claim with no contain owner timed for after hours.
- A last-scan date that expired when the policy changed.
- A count that assumes the same identity and network path as the drawing.
A tile is not detect scope. A percentage is not a contain owner. The useful question is not “How green are the agents?” It is “Which detect scope, contain owner, after-hours act, and evidence rows must be true before we treat this as an endpoint provider eval, and what proof would we accept?”
The managed cybersecurity provider evaluation page is the right place to reset the provider decision before you argue about a tile.
Separate the count from the provider eval
A green agent count does not show whether the endpoint program is operable.
Important questions remain open even when the tile looks green:
- What is in detect scope — workstations, servers, BYOD, OT — and what is known-unknown?
- Who owns contain and isolation when an agent is still green but the host is wrong?
- Who acts after hours, and what they leave as evidence?
- How offline and exception hosts are noticed, and who owns the fix?
- What policy and identity path must be true when every agent is at the count?
- What evidence means accepted — a green tile, a ticket, or a named containment exercise?
A count cannot answer these questions because it is not designed to capture them.
Compare the count with the evaluation brief
| Decision area | What a green agent count may show | What the endpoint provider eval must document |
|---|---|---|
| Decision identity | A healthy % tile | Whether this is a keep, replace, or failed-incident fix |
| Detect scope | Console screenshot | Endpoints in scope, exceptions, and known gaps |
| Contain | Silent or “auto” | Owner timed for isolation and after-hours act |
| Exceptions | Often hidden | Offline / BYOD / OT rows and who owns them |
| Evidence | Last scan date | Artifacts a later reviewer can open without a sales call |
| Acceptance | “All green” | Containment or tabletop proof a reviewer signs |
Two counts can show the same healthy percentage and still describe different programs. One may have contained a real host at load. The other may have screenshotted a quiet Tuesday.
Write the brief before you treat the count as done
Start with the work, not the percentage.
Write one record for the endpoint security provider evaluation:
- Decision identity: keep, replace, or failed-incident fix; why now; who owns the outcome.
- Detect scope a security owner would recognize, not a legend.
- Contain and after-hours owners, including what evidence they leave.
- Exception rows for offline, BYOD, and OT that still count as in program.
- Acceptance: the exercise that proves containment, not only the tile.
The managed cybersecurity meaning page is the companion when the open question is still what “managed” includes. The managed detection and response requirements and MSSP providers pages are companions when detect-and-respond ownership still sits next to the endpoint buy.
Questions that belong in the first meeting
Ask the incumbent or a challenger to show, not describe:
- Which hosts they treated as in scope, and which they treated as “the green count already proves it.”
- A contain owner timed for after hours, not a console screenshot.
- Exception rows for offline and BYOD that still have an owner.
- What a later reviewer would receive as evaluation proof — not a green agent count and a promised cyber week.
If those answers are a green agent count and an “all green” slide, you do not have an endpoint security provider evaluation. You have a tile.
What this page is not
This is not an EDR ranking, not an endpoint product sheet, and not a claim that The Data Partner already hardened anyone’s fleet after a catalog view. Skip incentive talk and skip any suggestion that a healthy-agent tile defines an eval. Write detect scope, contain ownership, exceptions, and acceptance for the provider you are buying. Then use the live companions, or contact The Data Partner on that packet. Broader buying questions sit on the FAQs page.